On Launch Llama
NeuralTrust - Enterprise AI Agent Security Platform
For security teams: NeuralTrust protects AI agents and applications from attacks, hallucinations, and data leakage through real-time runtime security and policy enforcement.
Built by Rodrigo Fernandez
Artificial Intelligence Developer Tools SaaS Freemium
Visit website → Upvotes · 0
In category: #2789 of 2807 · Artificial Intelligence
NeuralTrust is a Community listing on Launch Llama with 0 total upvotes, founded by Rodrigo Fernandez who joined in Oct 2026, compared against 6 alternatives.
Community listing
Listing status
0upvotes
Community score
Rodrigo Fernandez (Joined Oct 2026)
Founder
Compared against 6 alternatives
Market comparison
Real numbers
90d
-
2
Views
-
0
Visitors
-
0
Clicks
Public Launch Llama traffic for this listing.
Key Features
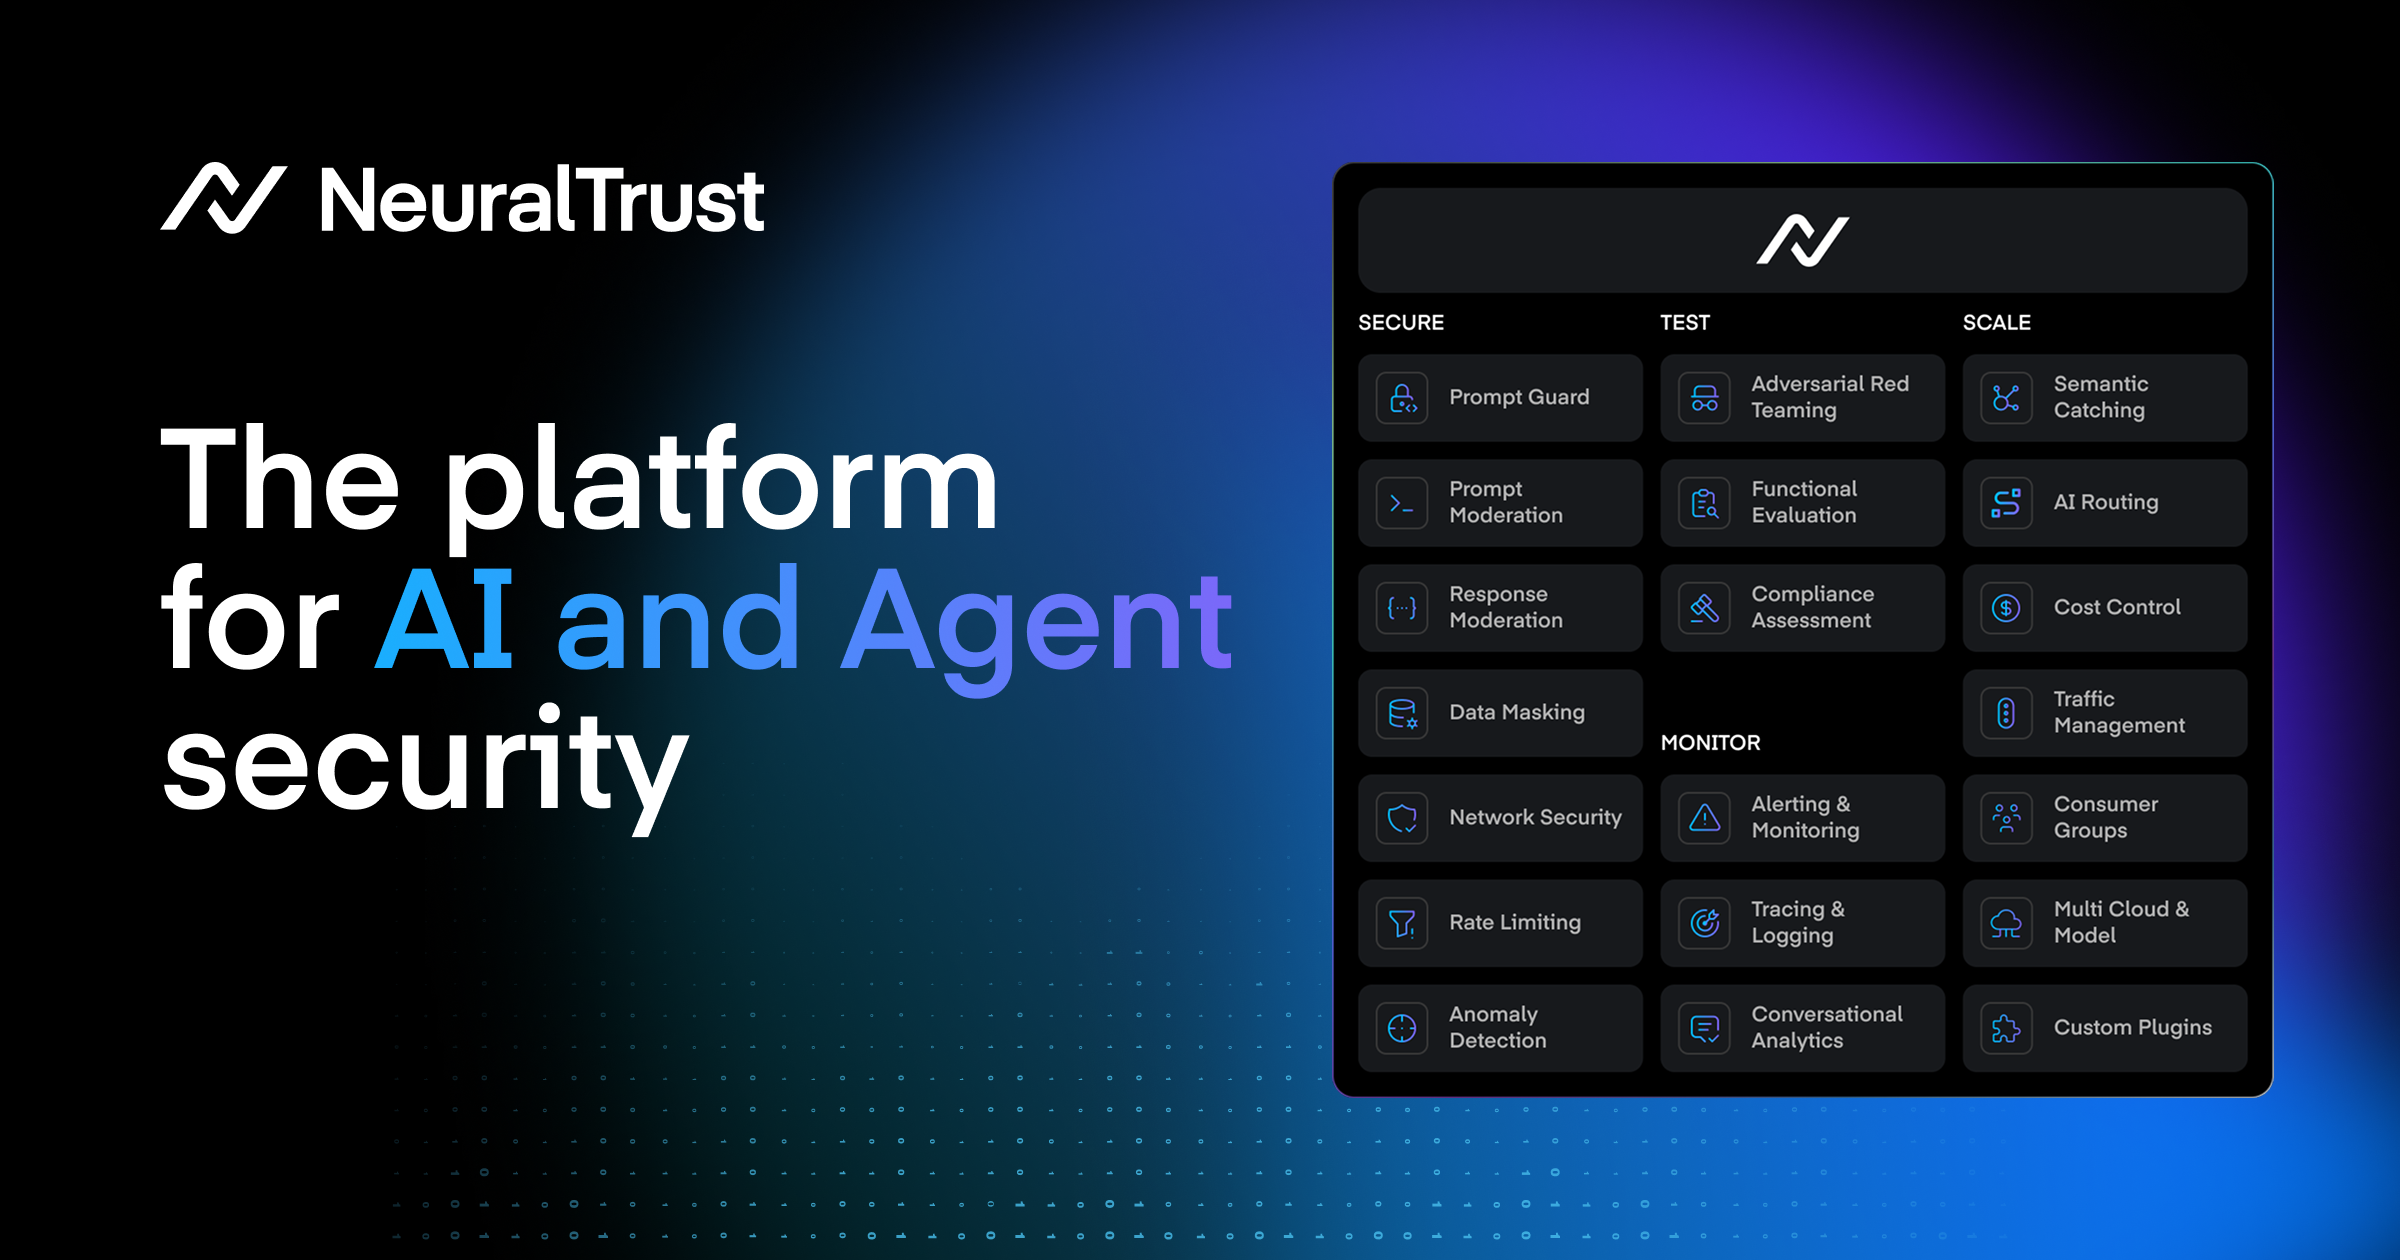
- Real-time agent runtime security to block attacks and data breaches as they occur
- Identity-aware gateway connecting agents to models, MCPs, and APIs securely
- Discover and govern deployed agents with complete visibility across teams and platforms
- Red-team models with adversarial attacks to identify vulnerabilities before production
- Deploy on-premise, SaaS, or hybrid with split-plane architecture and data sovereignty
- 99% multilingual detection using behavioral and multi-turn contextual analysis
About
NeuralTrust secures autonomous agents across homegrown, SaaS, and endpoint deployments with a specialized security layer that monitors prompt-response interactions and tool calls in real time. The platform combines agent discovery and posture management with behavioral analysis to detect and block attacks at sub-100ms latency, while maintaining EU AI Act compliance and supporting on-premise or hybrid deployment models. It processes 20K+ requests per second per node and has blocked 3M+ attacks across 1000+ monitored AI applications.
Pricing
NeuralTrust offers a free plan plus paid tiers. See the website for current pricing.
Verdict
In the competitive artificial intelligence space, NeuralTrust stands out as a solid option. It's gaining traction among founders who value simplicity and results. NeuralTrust secures autonomous agents across homegrown, SaaS, and endpoint deployments with a specialized security layer that monitors prompt-response interactions and tool calls in real time. If for security teams: neuraltrust protects ai agents and applications from attacks, hallucinations, and data leakage through real-time runtime security and policy enforcement is a priority for your team, it's worth giving NeuralTrust a closer look.
FAQ
What is NeuralTrust?
NeuralTrust secures autonomous agents across homegrown, SaaS, and endpoint deployments with a specialized security layer that monitors prompt-response interactions and tool calls in real time. The platform combines agent discovery and posture management with behavioral analysis to detect and block attacks at sub-100ms latency, while maintaining EU AI Act compliance and supporting on-premise or hybrid deployment models. It processes 20K+ requests per second per node and has blocked 3M+ attacks across 1000+ monitored AI applications.
Who should use NeuralTrust?
NeuralTrust is a strong fit if you are one of: • teams adopting AI-powered workflows and automation • developers, engineers, and technical founders • SaaS founders and subscription-based businesses If that does not sound like you, skim the features and site before committing time.
What problem does NeuralTrust solve?
NeuralTrust is built around this outcome: For security teams: NeuralTrust protects AI agents and applications from attacks, hallucinations, and data leakage through real-time runtime security and policy enforcement. Use the site demo or docs to confirm it matches the bottleneck you are trying to remove.
What are the main features of NeuralTrust?
NeuralTrust includes: • Real-time agent runtime security to block attacks and data breaches as they occur • Identity-aware gateway connecting agents to models, MCPs, and APIs securely • Discover and govern deployed agents with complete visibility across teams and platforms • Red-team models with adversarial attacks to identify vulnerabilities before production • Deploy on-premise, SaaS, or hybrid with split-plane architecture and data sovereignty • 99% multilingual detection using behavioral and multi-turn contextual analysis
Is NeuralTrust free to start?
NeuralTrust offers a free plan plus paid tiers. See the website for current pricing. Check the official site before you buy so you see current plans, trials, and limits. Most freemium tools let you validate the workflow before upgrading — check what the free tier unlocks for your use case.
How much does NeuralTrust cost?
NeuralTrust offers a free plan plus paid tiers. See the website for current pricing. Check the official site before you buy so you see current plans, trials, and limits.
How does NeuralTrust use AI?
NeuralTrust uses AI as part of its workflow. Before relying on it for customer-facing or confidential work, confirm what data is sent to models, whether outputs are editable, and how you can review results.
Is NeuralTrust worth trying?
It promises: For security teams: NeuralTrust protects AI agents and applications from attacks, hallucinations, and data leakage through real-time runtime security and policy enforcement. Worth trying if that problem is painful for you this week; skip it if you only need a one-off workaround you already have.
How do I try NeuralTrust?
Open the official NeuralTrust website from this page, run the smallest real task you care about (not a toy demo), and decide in one session whether it removes friction. Check pricing and data/privacy terms before you put production work into it.
Alternatives
- AI Security Guard
For AI teams: AI Security Guard blocks jailbreaks and prompt injection attacks in real time so your agents stay protected from malicious inputs.
- Privatevault.ai
For enterprises: PrivateVault enforces runtime allow/review/block controls on autonomous AI agents, adding governance between intent and execution.
- Agyn
For teams: Agyn runs AI agents in secure sandboxes with spend caps and audit trails so your organization can deploy agents safely without security or finance risk.
- Autonomous AI Agents for Cybersecurity
For security teams: Autonomous AI agents detect threats, protect your brand, and manage attack surface so you reduce manual monitoring and compliance work.
- Harden
For engineering teams: Harden secures AI coding agents by checking tool calls before execution, keeping your repo and outputs local while preventing malicious actions.
- ClawSecure
For AI developers: ClawSecure scans and monitors AI agents in real-time with full OWASP ASI coverage, sub-200ms verification, and no signup required.
Ask AI
ChatGPT Claude Perplexity Grok
For agents
llms.txt · llms-full.txt · ai.txt · Live fact sheet · Full catalog (.md) · Endpoint index · API spec · REST access · Agent server · Server manifest · Server discovery