On Launch Llama
Decloak
For AI builders: Decloak scans your shipped app for platform-specific security misconfigurations so you catch leaks before attackers do.
Built by Stephen Gray
Artificial Intelligence SaaS Freemium
Visit website → Upvotes · 56
In category: #1328 of 2739 · Artificial Intelligence
Decloak is a Community listing on Launch Llama with 56 total upvotes across 35 founder supporters, founded by Stephen Gray who joined in Aug 2026, compared against 6 alternatives.
Community listing
Listing status
56upvotes
Community score
Stephen Gray (Joined Aug 2026)
Founder
Compared against 6 alternatives
Market comparison
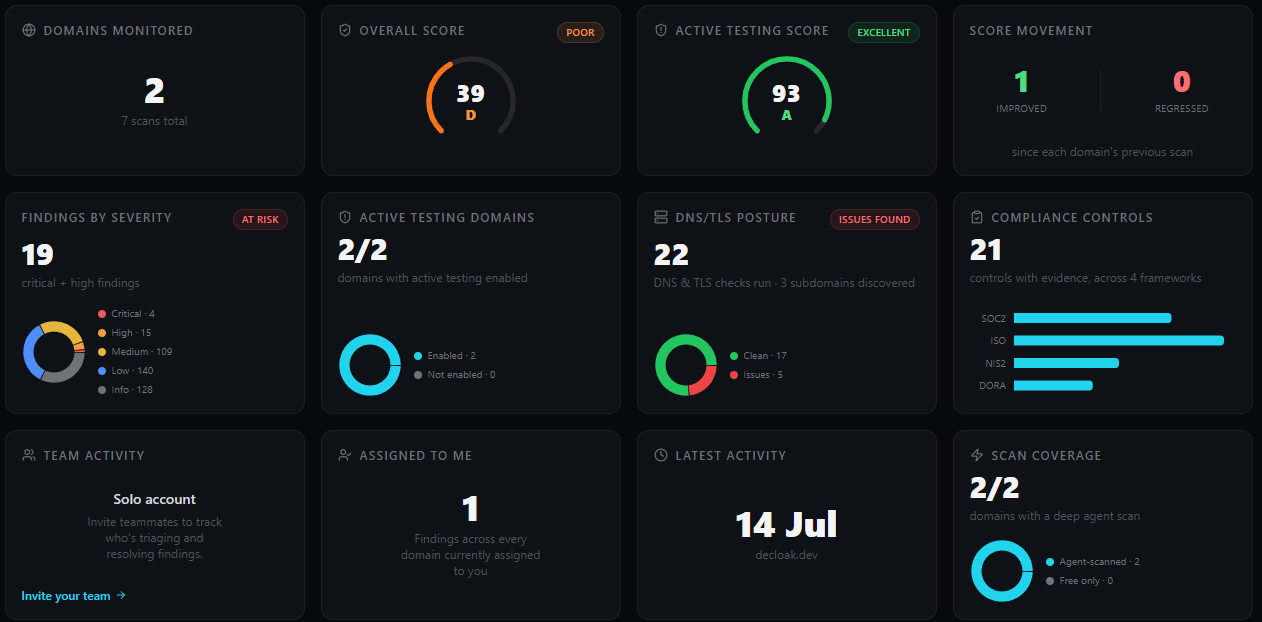
Key Features
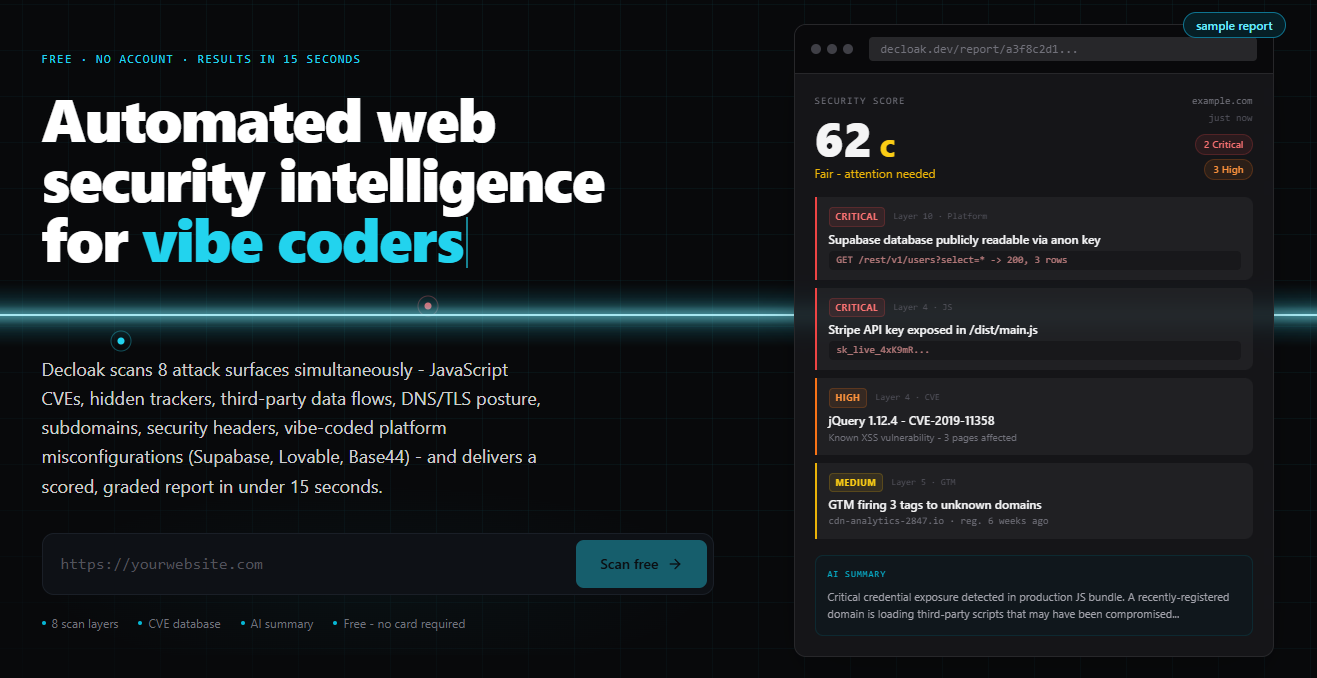
- Surfaces HTTP/TLS, HTML, JS CVEs, tag managers, and supply chain, correlated together for
- Delivers auto-detects Lovable, Supabase, Base44, Bubble, and Next.js, with checks specific to
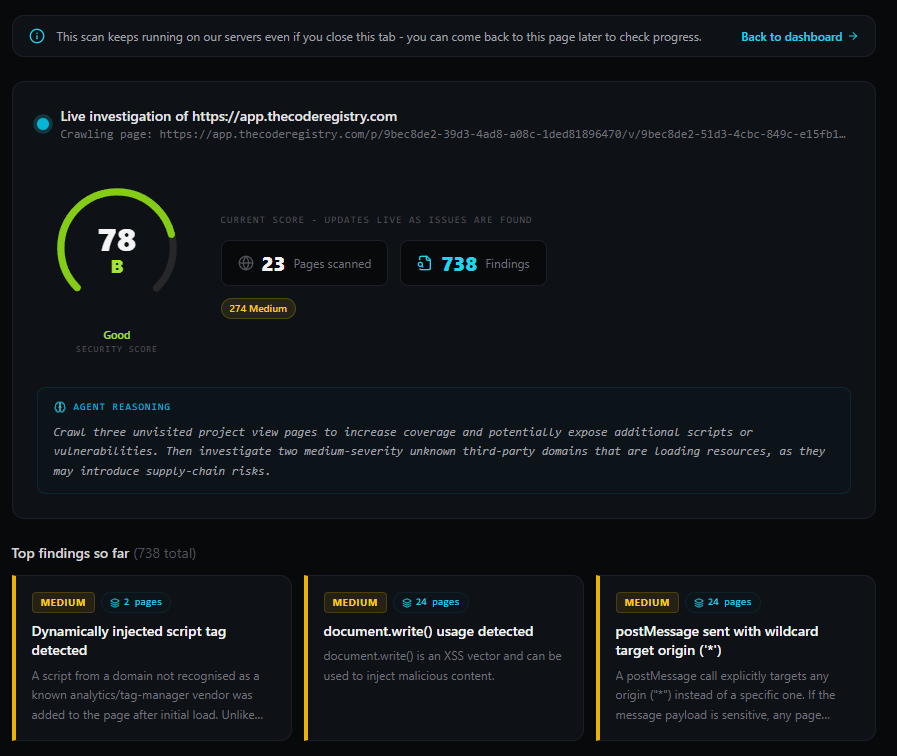
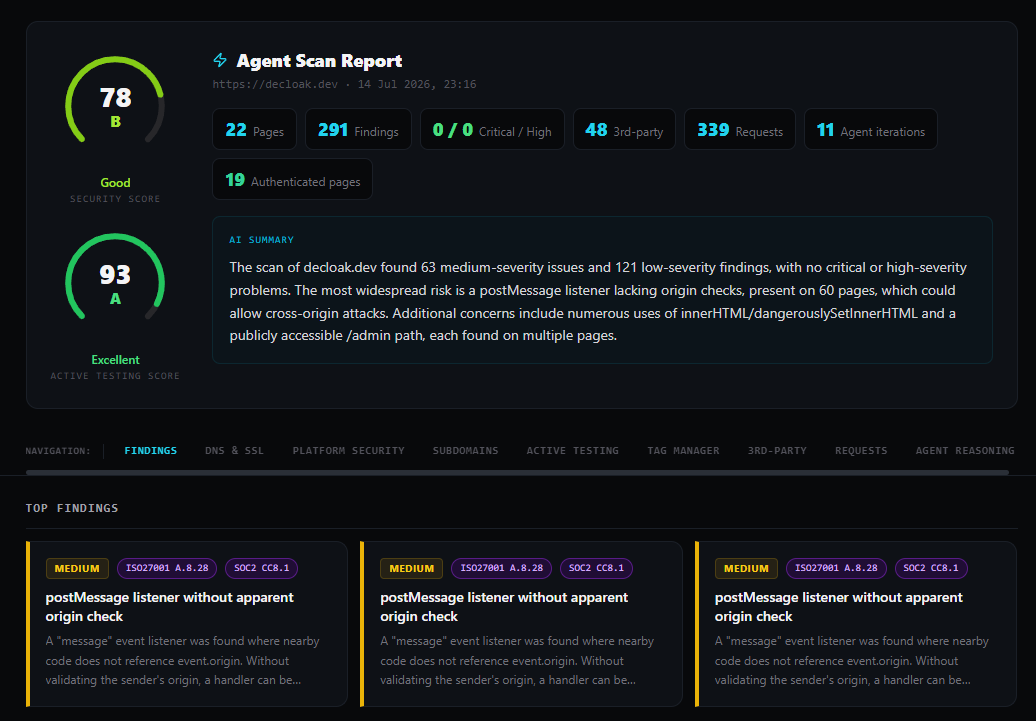
- Delivers paid AI agent investigates each finding, reconstructing exposed source code and
- Delivers pentesting and API testing (REST, GraphQL, SOAP) on Enterprise, confirming real
- Delivers sOC2, ISO 27001, NIS2, and DORA control mapping with exportable PDF evidence packages
- Delivers free single-page scan, no account or card required, results in 15 seconds
About
Vibe coding gets you from idea to live app in hours, but the security review is usually the first thing that gets skipped. Decloak is built to catch what shipping fast leaves behind. Paste your URL and Decloak automatically fingerprints your platform - Lovable, Supabase, Base44, Bubble, or Next.js - then checks for the specific misconfigurations known to affect each one. The most common failure it catches: a Supabase database left publicly readable because Row Level Security was never enabled, meaning anyone can read your data using your own public API key. It also flags leaked Supabase service_role keys sitting in client-side JavaScript, exposed Stripe and other API keys in production bundles, and known platform CVEs like the Next.js middleware authorization bypass. Every scan runs a full 8-layer analysis: HTTP/TLS, HTML, live network traffic, JavaScript CVEs, tag managers, third-party supply chain, platform misconfigurations, and AI synthesis, producing a weighted security score and A-F grade you can track over time. The free tier needs no account or card and returns results with an AI-written executive summary in 15 seconds. Most solo builders never need more than that. If you start shipping client work or need scheduled scans, PDF exports, compliance mapping, or MCP/API access for agent-triggered scans, paid tiers cover that, but the free tier is the whole pitch for solo builders.
Who it is for
Vibe coders and solo builders shipping AI-generated apps, small businesses needing real security without an enterprise budget, compliance and security teams needing SOC2/ISO 27001/NIS2/DORA evidence, and agencies or MSPs managing multiple client domains.
- Vibe coders and solo builders shipping apps with Lovable, Supabase, Base44 etc
- Small and growing businesses that need real security posture which is affordable
- Compliance and security teams that need SOC2, ISO 27001, NIS2, or DORA evidence
- Agencies and MSPs managing security across multiple client domains
Use Cases
- Paste shipped app URL for instant security fingerprint and A-F grade; no account needed, results in 15 seconds with AI executive summary
- Scan for platform-specific misconfigurations: Row Level Security gaps in Supabase, exposed API keys in bundles, leaked service_role keys, known CVEs
- Set up scheduled scans on paid tiers to catch new security drift over time, tracking your weighted security score as you ship updates to production
- Enable MCP/API access on paid plans to trigger Decloak scans programmatically from agents or CI/CD pipeline, automating security checks
- Export PDF compliance reports from paid tiers to document security posture for clients or stakeholders when shipping production work
Pricing
Decloak offers a free single-page scan with no account or card required. Paid plans start at Starter, scaling up through Pro to Enterprise, unlocking full-site AI agent investigation, compliance mapping, and AI pentesting as you go. Full pricing details are available on their official website.
Verdict
In the crowded web security and compliance scanning space, Decloak stands out by covering more ground with one tool rather than requiring several. The free tier scans a single page in 15 seconds, no account or card required, and already checks for the misconfigurations most common to AI-generated apps built with Lovable, Supabase, Base44, and similar platforms, most notably a publicly readable database left exposed because Row Level Security was never turned on. Paid tiers scale up from there. Instead of running a fixed checklist, the AI agent investigates each finding it turns up, following threads across the whole site, reconstructing exposed source code, and cross-referencing suspicious domains. Enterprise adds AI pentesting and API endpoint testing, confirming real exploitability with sandboxed tooling rather than just flagging plausible risk. For compliance and security teams, findings map automatically to SOC2, ISO 27001, NIS2, and DORA controls, with exportable PDF evidence packages, at a fraction of what teams currently pay for tools like AppCheck or Qualys. If you shipped fast and want to make sure security kept up, Decloak is worth a closer look.
FAQ
What is Decloak?
Vibe coding gets you from idea to live app in hours, but the security review is usually the first thing that gets skipped. Decloak is built to catch what shipping fast leaves behind. Paste your URL and Decloak automatically fingerprints your platform - Lovable, Supabase, Base44, Bubble, or Next.js - then checks for the specific misconfigurations known to affect each one. The most common failure it catches: a Supabase database left publicly readable because Row Level Security was never enabled, meaning anyone can read your data using your own public API key. It also flags leaked Supabase service_role keys sitting in client-side JavaScript, exposed Stripe and other API keys in production bundles, and known platform CVEs like the Next.js middleware authorization bypass. Every scan runs a full 8-layer analysis: HTTP/TLS, HTML, live network traffic, JavaScript CVEs, tag managers, third-party supply chain, platform misconfigurations, and AI synthesis, producing a weighted security score and A-F grade you can track over time. The free tier needs no account or card and returns results with an AI-written executive summary in 15 seconds. Most solo builders never need more than that. If you start shipping client work or need scheduled scans, PDF exports, compliance mapping, or MCP/API access for agent-triggered scans, paid tiers cover that, but the free tier is the whole pitch for solo builders.
Who is Decloak for?
Vibe coders and solo builders shipping AI-generated apps, small businesses needing real security without an enterprise budget, compliance and security teams needing SOC2/ISO 27001/NIS2/DORA evidence, and agencies or MSPs managing multiple client domains. • Vibe coders and solo builders shipping apps with Lovable, Supabase, Base44 etc • Small and growing businesses that need real security posture which is affordable • Compliance and security teams that need SOC2, ISO 27001, NIS2, or DORA evidence • Agencies and MSPs managing security across multiple client domains
What problem does Decloak solve?
Decloak is built around this outcome: For AI builders: Decloak scans your shipped app for platform-specific security misconfigurations so you catch leaks before attackers do. Use the site demo or docs to confirm it matches the bottleneck you are trying to remove.
How to set up scheduled scans on paid tiers to catch new security drift over time, tracking your weighted security score as you ship updates to production?
Decloak is set up for this: Set up scheduled scans on paid tiers to catch new security drift over time, tracking your weighted security score as you ship updates to production. Open the official site from this page and run that workflow on a real task to confirm fit.
What are the main features of Decloak?
Decloak includes: • 8-layer scan: HTTP/TLS, HTML, JS CVEs, tag managers, and supply chain, correlated together for risks single-layer tools miss • Auto-detects Lovable, Supabase, Base44, Bubble, and Next.js, with checks specific to each platform's most common failure • Paid AI agent investigates each finding, reconstructing exposed source code and cross-referencing suspicious domains • AI pentesting and API testing (REST, GraphQL, SOAP) on Enterprise, confirming real exploitability with sandboxed tooling • SOC2, ISO 27001, NIS2, and DORA control mapping with exportable PDF evidence packages • Free single-page scan, no account or card required, results in 15 seconds
Is Decloak free to start?
Decloak offers a free single-page scan with no account or card required. Paid plans start at Starter, scaling up through Pro to Enterprise, unlocking full-site AI agent investigation, compliance mapping, and AI pentesting as you go. Full pricing details are available on their official website. Most freemium tools let you validate the workflow before upgrading — check what the free tier unlocks for your use case.
How much does Decloak cost?
Decloak offers a free single-page scan with no account or card required. Paid plans start at Starter, scaling up through Pro to Enterprise, unlocking full-site AI agent investigation, compliance mapping, and AI pentesting as you go. Full pricing details are available on their official website.
What are the best alternatives to Decloak?
People comparing options often look at Snyk, Semgrep, OWASP ZAP, Wiz, Socket.dev. Pick based on workflow fit, pricing, and how painful migration would be — not just feature checklists.
Is Decloak private and safe for my files?
Decloak's positioning emphasizes keeping work local or private (for example browser-side processing or limited uploads). Still verify the privacy policy and data handling on the official site for your compliance needs.
Do I need an account to use Decloak?
Decloak highlights getting started without a heavy signup funnel. Confirm on the website whether advanced features still require an account.
Alternatives
- Decloak.dev
For developers: Decloak scans your web app across 8 attack surfaces in seconds so you fix security gaps before they become breaches.
- VibeScan
For developers: VibeScan detects security flaws in AI-built apps—exposed keys, CORS issues, missing rate limits—in seconds, no signup needed.
- Vibetoolstack
For indie hackers and solo founders: Vibetoolstack curates real dev tools and tech stacks with honest reviews, helping you skip AI-slop and build efficiently.
- VibeDoctor
Security and code quality scanner for AI-generated applications. Runs 149+ automated checks across source code and deployed sites, ranking findings by severity with actionable fixes in under 2 minutes
- Debuggix
For developers shipping fast: Debuggix runs 9 security scanners in parallel, then AI generates working code patches for every finding.
- VibeKit
For developers: VibeKit builds and hosts mobile apps with persistent AI agents that improve over time, so you ship faster from your phone.
Supporters
35 founders35 founders contributed 56 upvotes to Decloak on Launch Llama.




Reviews
2 comments
Thanks! It was originally a replacement for existing VERY expensive security tools for businesses, like AppCheck, then it kept evolving from there. In the World of AI code generation, security is even more important, it should be easier than ever to keep on top of your security. It shouldn't be complex and overly expensive.
Hey, love seeing this here! 👋 What inspired you to build this? Would love to hear the story behind it.
Ask AI
ChatGPT Claude Perplexity Grok
For agents
llms.txt · llms-full.txt · ai.txt · Live fact sheet · Full catalog (.md) · Endpoint index · API spec · REST access · Agent server · Server manifest · Server discovery